Security & Access Management
Deciding who can reach what
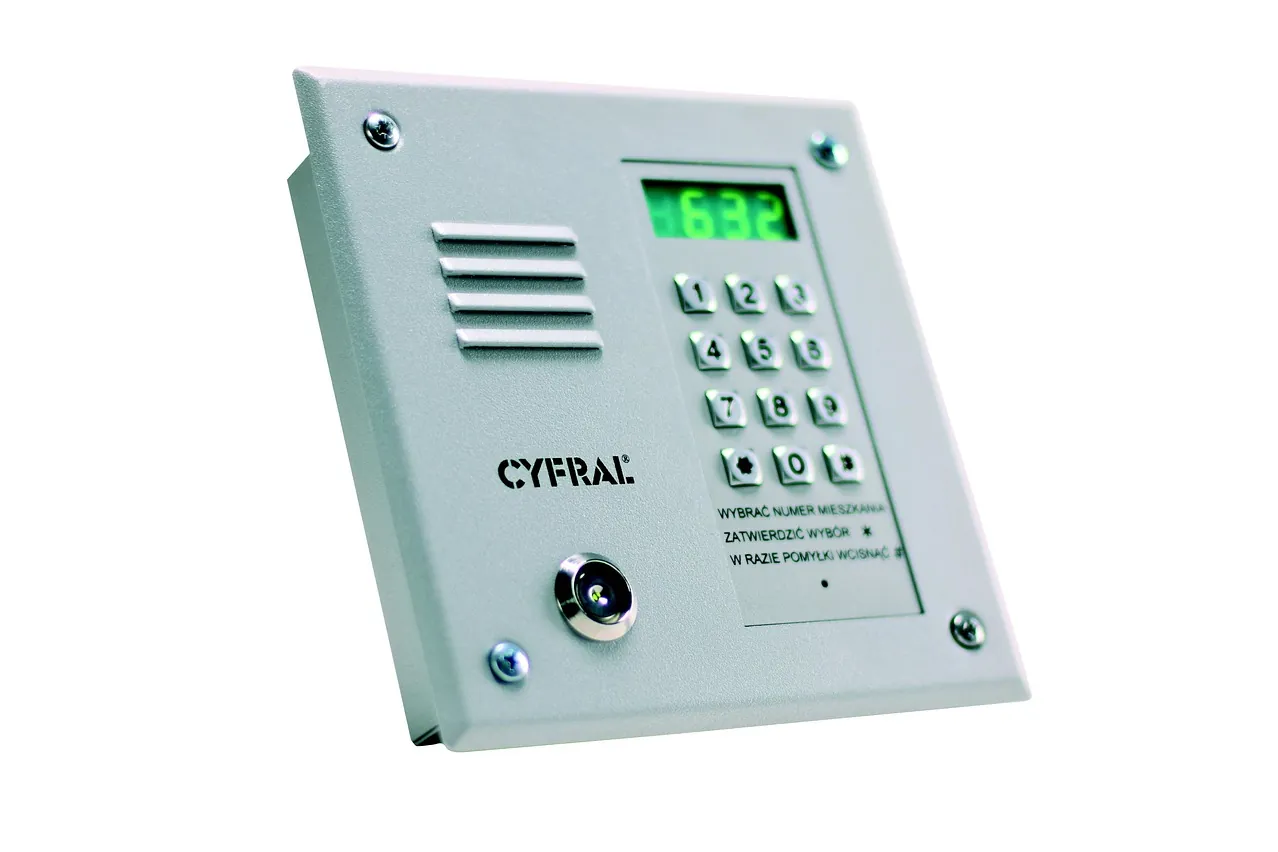
Accounts, passwords and permissions arranged so people hold exactly the access their job needs, and leavers lose it that day.
Photo: WFranz / Pixabay 
Photo: gcleaves / Pixabay
Selected work demonstrating this service.
-
Wrote 1,000 RBAC rules to secure Linux servers
Enhanced data security by implementing 1,000 RBAC rules for developers, application instances, PostgreSQL, MS SQL, and other Linux servers, preventing unauthorized access; documented with Ansible automation.
-
Led access management across M365 and SSO
Prevented security breaches by leading access management initiatives, utilizing M365, 1Password, Red Hat SSO, and OKTA SSO.
-
Managed 8 WireGuard and IPsec VPN connections
Managed and troubleshot 8 WireGuard VPN and IPsec VPN connections, ensuring secure communication across Google Cloud and Linux systems.
-
Improved team communication and collaboration
Improved team communication and collaboration by implementing Slack, Mattermost, 1Password, and Jira, saving 8,000 hours of labor.
-
Administered network infrastructure
Administered network infrastructure for over 1,000 servers, ensuring optimal system deployment, security, and troubleshooting.
-
Automated SSL/TLS certs for 100 Docker apps
Automated SSL/TLS certificate creation for 100 Docker applications, ensuring secure connections across Ubuntu Linux hosts.
-
Built organization context switching for users
Designed an organization context‑switching system with client localStorage and server‑side cookie mirroring, letting users act as managed organizations while enforcing least‑privilege authorization.
-
Built email with failover and delivery logging
Built email as a platform capability — three providers with failover, delivery webhooks, send and delivery logging, templating and campaigns — behind a startup check that will not boot without one.
-
Provisioned Azure infrastructure as code
Provisioned Azure infrastructure as code with Bicep — Container Apps, PostgreSQL Flexible Server, Front Door/WAF and networking — across the development, staging and production environments.
-
Hardened the application with nonce‑based CSP
Hardened the application with nonce‑based CSP, HSTS, SameSite cookies, least‑privilege database roles and server‑side entitlement re‑checks.
-
Automated team collaboration
Automated team collaboration, password management, task and time management, and built a semi‑automatic project‑showcase system, raising team productivity.
-
Integrated a company‑wide password manager
Integrated a company‑wide password‑management system, strengthening security and streamlining access control.
-
Built Stripe and in‑app purchase entitlements
Built the payments and entitlements layer — Stripe alongside Apple and Google in‑app purchase — gating the directory, search and export through an 11‑table access model checked on the server.
-
Built fail‑closed rate limiting and anti‑abuse
Built fail‑closed abuse controls — 22 Redis‑backed rate limiters, Cloudflare Turnstile, request idempotency and an origin lock — so the platform sheds bots and floods instead of trusting its callers.
-
Built company ownership claims and adjudication
Built company ownership claims end to end — a user claims a company, an administrator adjudicates, and an approval rewrites the authorization graph that decides who is allowed to edit what.
-
Ran a continuous security scanning programme
Established a continuous security programme — code scanning, DAST, dependency and vulnerability checks, SBOM generation, secret scanning and SHA‑pinned actions — alongside 21 written security audits.
-
Three locks on the door, none of them locked
Found and closed three SSH brute‑force protections that had never worked: a ban jail watching port 22 while the daemon listened on 1986, a rate limit shadowed by a broader rule above it, and a ban action whose binary never resolved, so no ban had ever applied.
-
Hardened SSH to 24 validated directives
Hardened SSH to 24 asserted directives with three‑stage validation — the candidate file, the assembled config, then the daemon's own read‑back — after the read‑back caught the running server silently overriding two of the twenty‑four.
-
Proved the intrusion ban works every run
Proved the intrusion‑banning path end to end on every hardening run by banning a reserved test address, reading the resulting kernel rule and unbanning in a guaranteed cleanup block, so a jail that stops working fails a run instead of reporting healthy.
-
Verified firewall rules by position
Verified firewall rules by position rather than presence, reading the numbered rule list and the live packet‑filter chain, because a rule that exists is not a rule any packet reaches.
-
Added a one‑second preflight for secrets
Added a preflight play that runs the same code as the converge against operator‑local secrets in about a second, after a half‑applied production run died on its ninth task with the swap settings already written to the live host.
-
Reconciled a 20‑record DNS zone as code
Reconciled a 20‑record DNS zone declaratively against the Cloudflare API with separate audit and BIND‑export entry points, and turned the CDN proxy back off on privacy grounds after building it.
-
Cut systemd sandbox exposure on every unit
Cut systemd sandbox exposure across every unit this platform installs — a dead‑man's‑switch service from 9.6 UNSAFE to 1.5, an internet‑facing git forge from 8.3 EXPOSED to 1.5 — and added a converge‑time parser check after finding a misspelled directive silently ignored in three unit templates.
-
Ran containers on Podman and Quadlet
Deployed a container plane on Podman and Quadlet under systemd rather than Docker, because Docker publishes container ports above the host firewall's own rules — and gave deploys an unprivileged user with one fixed command instead of root.
-
Provisioned a second server from code
Automated the provisioning of a second server on a second cloud provider, creating the firewall before the machine so it is born behind one, with both providers' firewalls written directly against their REST APIs to avoid a third‑party collection.
-
Wrote a scope rule after a credential leak
Wrote a scope rule into the repository after a restructure carried another company's inventory, firewall allowances and prose into it — and kept the quarantined residue under the secret scanner rather than excluding it.
-
Split every operational secret per host
Split the four per‑host operational secrets after establishing that two hosts sharing one dead‑man's switch alert less than two switches, not more, and that a shared backup passphrase makes two hosts one repository.
-
Reached the unused half of the core
Reached the half of the messaging core the application had never used — backup transfer, disappearing messages, message editing and resending, verified invitations, proxies and encryption policy — driving every test against the real library with no mocks.
-
Know the licence of everything you ship
Audited 644 Rust crates for licence compatibility on every build, and proved the check fires by rewriting one crate's licence and by moving the pinned core revision without regenerating.
-
Measured 13 addresses with no tracking
Measured thirteen addresses from the web server's own access log alone — no cookie, no tracker and no third‑party service — masking the client network as each line is written, and folding the result into a permanent archive of 21 daily counts and 20 monthly facets.
-
Published a readable Tor onion mirror
Published the site as a Tor onion mirror on a readable address beginning engineer, with the key generated off the host so it never reached this repository or a laptop, and left it the one front door of four that is never counted.
If this is the work you need done, the next step is a conversation.
Tell us the problem and we will tell you honestly whether we are the right people.