Networking & VPN
13 achievements
Photo: doctor-a / Pixabay 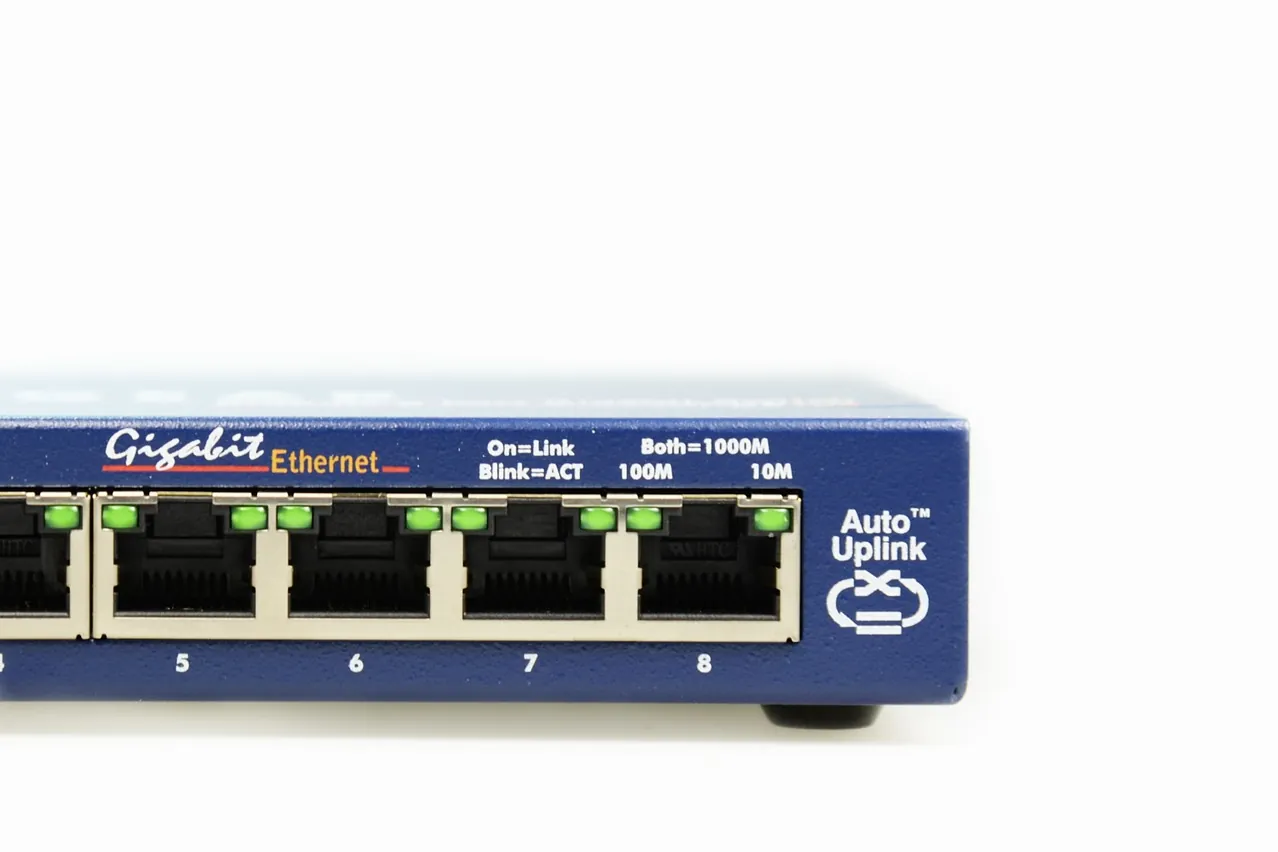
Photo: blickpixel / Pixabay
-
Designed and ran 6 ETL/ELT pipelines
Designed, implemented, and administered 6 ETL/ELT pipelines, utilizing Google BigQuery, MSSQL, PostgreSQL, Shell scripting, PL/pgSQL, and Transact‑SQL, integrating data for efficient Python API processing.
-
Managed 30 Ubuntu Linux VPS instances
Managed 30 Ubuntu Linux VPS instances, implementing disaster recovery strategies and ensuring optimal network configurations.
-
Managed 8 WireGuard and IPsec VPN connections
Managed and troubleshot 8 WireGuard VPN and IPsec VPN connections, ensuring secure communication across Google Cloud and Linux systems.
-
Administered network infrastructure
Administered network infrastructure for over 1,000 servers, ensuring optimal system deployment, security, and troubleshooting.
-
Configured and deployed 1,000 Wi‑Fi routers
Configured and deployed 1,000 Wi‑Fi routers, improving network accessibility and performance for clients.
-
Administered 100 Bare Bone servers
Administered 100 Bare Bone servers, physical networks, and IP telephony systems, ensuring robust infrastructure for company growth.
-
Provisioned Azure infrastructure as code
Provisioned Azure infrastructure as code with Bicep — Container Apps, PostgreSQL Flexible Server, Front Door/WAF and networking — across the development, staging and production environments.
-
Ran 24/7 support for ~1,000 IPTV/OTT servers
Provided round‑the‑clock 24/7 infrastructure support for an IPTV/OTT streaming platform, administering ~1,000 servers plus client‑owned systems for global customers in China, the US and Germany.
-
Kept IPTV streaming signals running non‑stop
Ensured uninterrupted delivery of IPTV streaming signals between suppliers and clients, monitoring and maintaining the streaming network and IP telephony around the clock.
-
Built fail‑closed rate limiting and anti‑abuse
Built fail‑closed abuse controls — 22 Redis‑backed rate limiters, Cloudflare Turnstile, request idempotency and an origin lock — so the platform sheds bots and floods instead of trusting its callers.
-
Three locks on the door, none of them locked
Found and closed three SSH brute‑force protections that had never worked: a ban jail watching port 22 while the daemon listened on 1986, a rate limit shadowed by a broader rule above it, and a ban action whose binary never resolved, so no ban had ever applied.
-
Verified firewall rules by position
Verified firewall rules by position rather than presence, reading the numbered rule list and the live packet‑filter chain, because a rule that exists is not a rule any packet reaches.
-
Reconciled a 20‑record DNS zone as code
Reconciled a 20‑record DNS zone declaratively against the Cloudflare API with separate audit and BIND‑export entry points, and turned the CDN proxy back off on privacy grounds after building it.
If this is the work you need done, the next step is a conversation.
Tell us the problem and we will tell you honestly whether we are the right people.
This work is part of what we offer as Networking & VPN Setup, System Administration, Security & Access Management, Site Reliability & Monitoring, AI Agent Security, Backend & API Development, Infrastructure as Code and IT Support & Helpdesk.
 Building something that needs this? Get in touch.